Illustrative exampleAI Threat Shield
An online retailer on an ageing PHP stack
- The situation
- A regional retailer runs its shop on WordPress with an out-of-support PHP version. Login pages see credential-stuffing bursts at night, and scrapers copy prices every few minutes. An upgrade is planned but months away.
- What SENTRA does
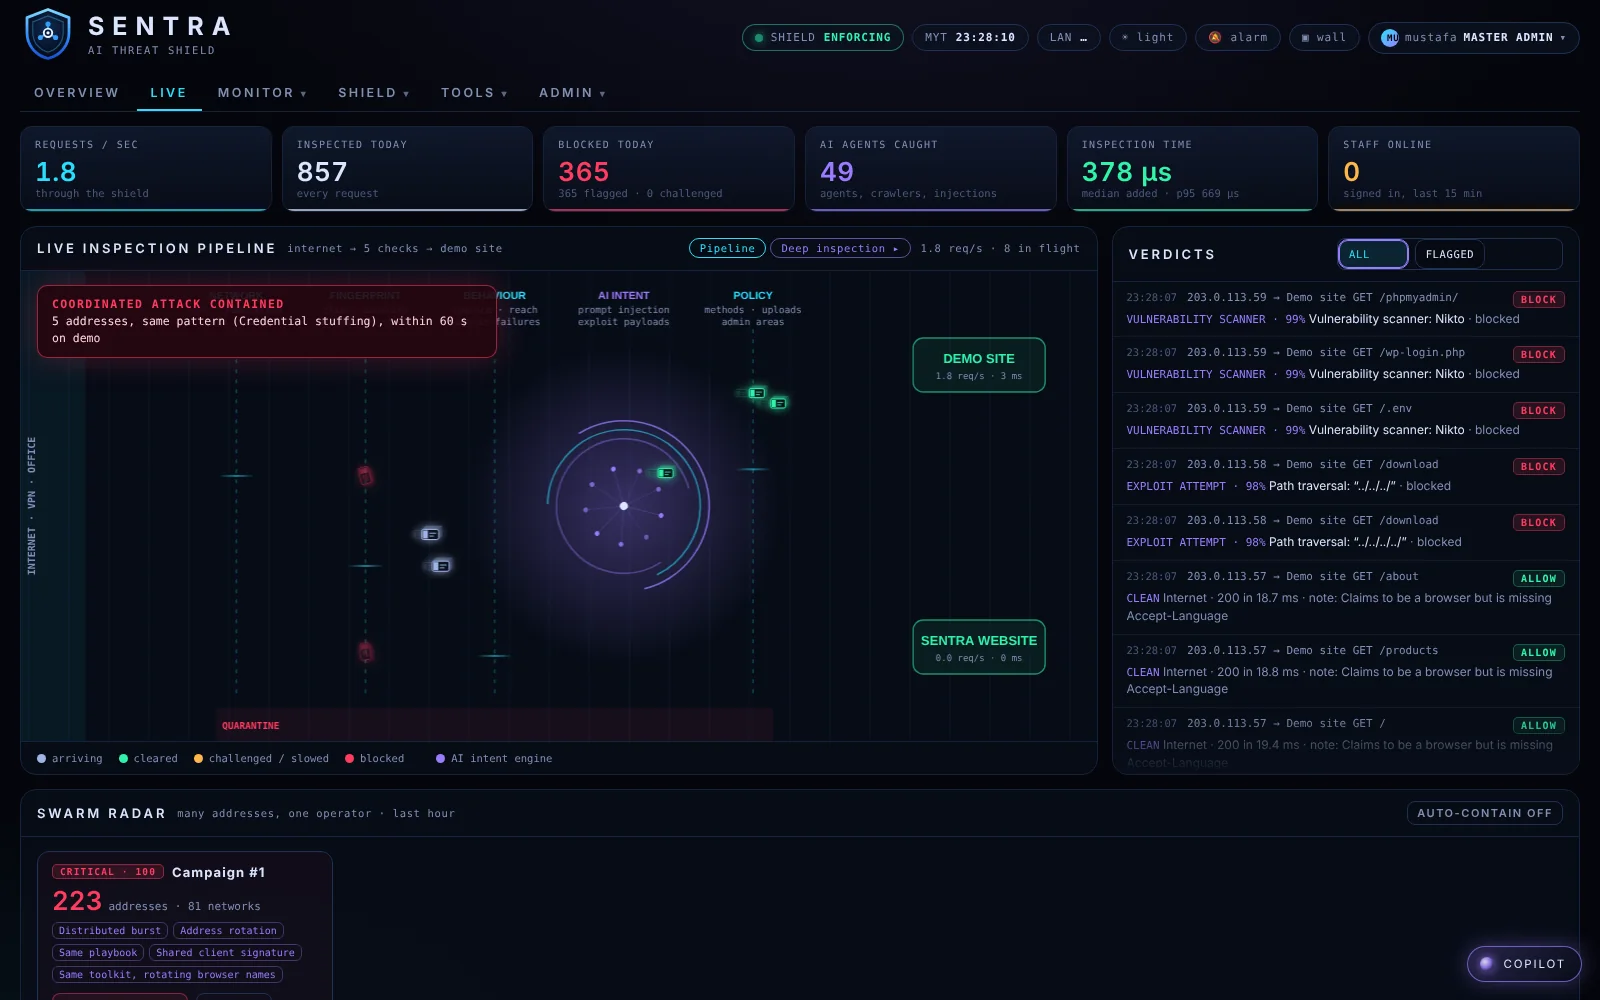
- AI Threat Shield goes in front of the shop as an edge node. A week in Monitor mode shows what would be stopped; then Enforce. Virtual patching blocks attempts against known PHP and plugin flaws, login bursts are contained, and missing security headers are added to every response.
- The outcome
- Attacks are stopped before the server, the team gets time to upgrade on its own schedule, and the Safety Check grade rises without code changes.